Everything you need to
hunt smarter
One platform for your entire bug bounty pipeline: projects and Starlark workflows, out-of-band interactions, templated payloads, and queryable datasets built by a hunter, for hunters.
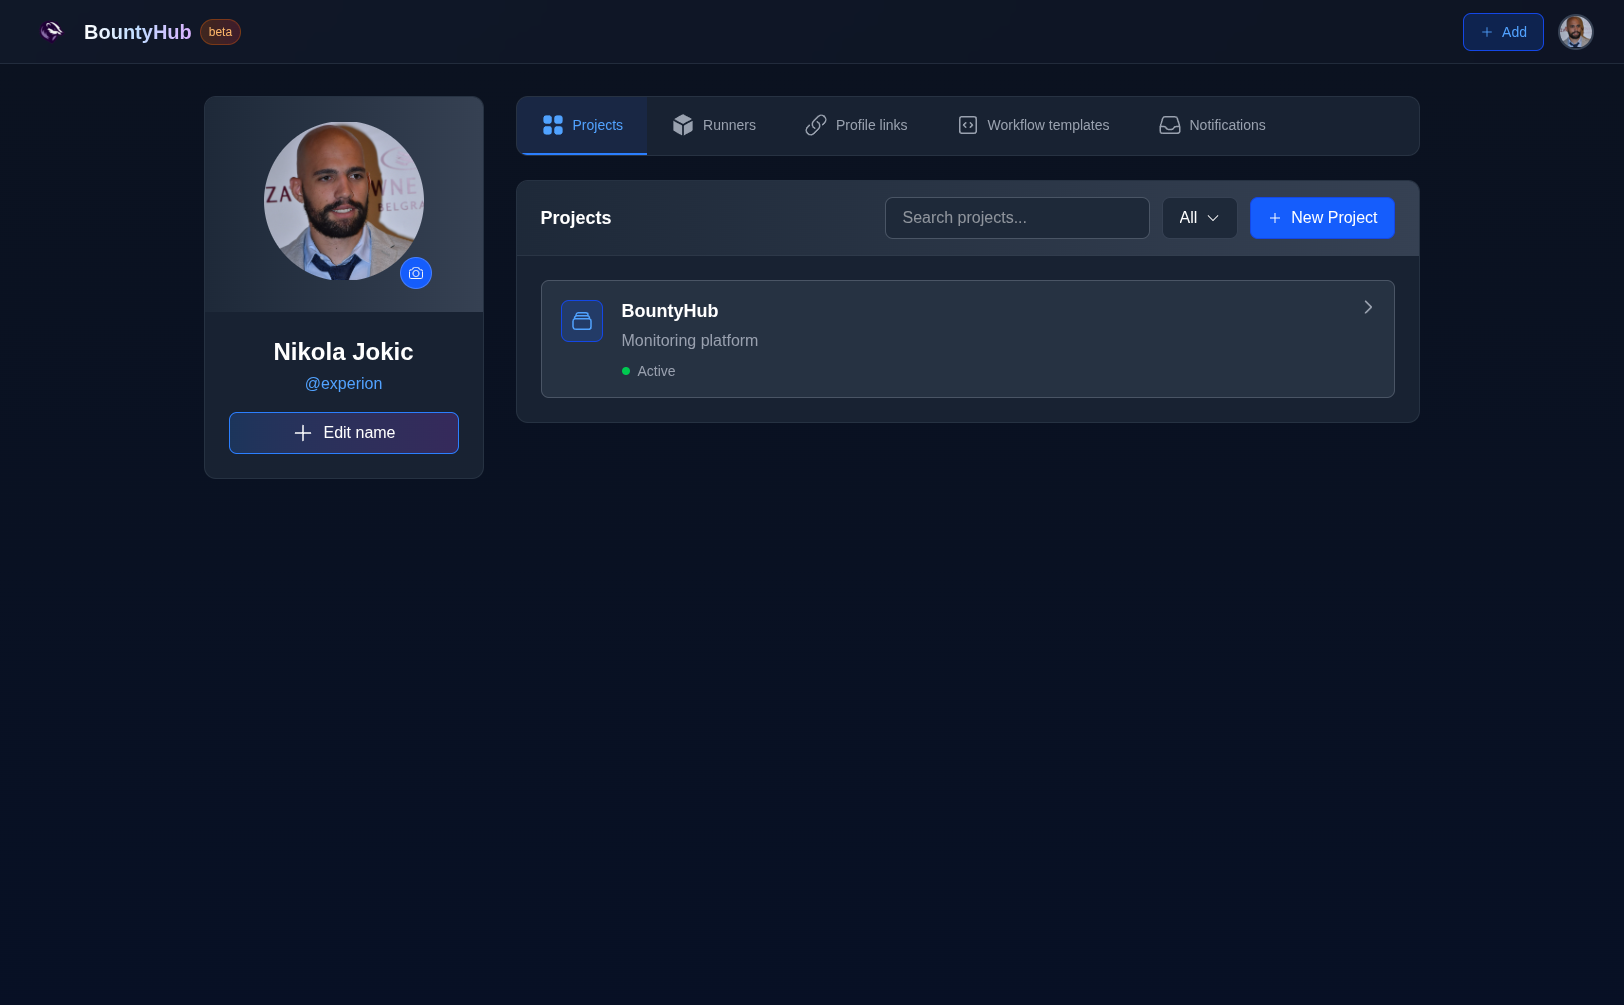
One home for every target you hunt
Each project maps to a program, domain, or asset. Reuse workflow templates and variables across targets, so starting on a new program takes minutes, not hours of setup.
Automate recon with CI/CD-style workflows
Write pipelines in BHW, a fully valid Starlark dialect, the same language family as Bazel. Version every workflow, roll back any time, and share proven templates so your best recon chains are one click away on every new target.
workflow( activities = [ activity( name = "discover", triggers = [trigger.cron("0 6 * * *")], steps = [ step.exec(command = ["subfinder", "-d", config.var("domain"), "-o", "subs.txt"]), step.transform( source = path.file("subs.txt").lines(), pipeline = transform.trim().lower().unique(), destination = path.file("subs-clean.txt"), ), step.update_dataset( table = "subdomains", source = path.file("subs-clean.txt").lines(), pipeline = transform.unique(), mapping = {"host": row.value}, mode = dataset.upsert(), ), ], ), activity( name = "triage", triggers = [trigger.on(discover.succeeded())], steps = [ step.agent( prompt = "Flag exposed admin panels on new hosts.", model = model("default"), provider = provider.key("anthropic/personal"), output = output.json(), ), ], ), ],)
Run any tool on your own infrastructure
Register runners on your machines and invoke them directly from your workflows. Install proprietary scanners and private tooling, and your arsenal never leaves your infrastructure.
Never miss a blind payload callback
bhlast is a self-hosted Burp Collaborator alternative built into BountyHub. Capture DNS and HTTP interactions, register custom DNS records for SSRF, and serve exploits from the built-in file server. Every interaction notifies you in real time.
rendered
'"><img src=//a1b2c3.oob.bountyhub.test>Build a payload arsenal and template it
Store payloads in reusable groups and template them with variables. Adapting wordlists, injection strings, and exploit payloads to each target takes seconds, not copy-paste sessions.
Turn findings into queryable datasets
Airtable-style tables for everything you discover: subdomains, open ports, CVE scan results, anything structured. Full upload history, and row-level triggers fire on insert, update, and soft-delete so your data reacts automatically.
| subdomain | status | source |
|---|---|---|
| api.target.com | 200 | recon-run #41 |
| dev.target.com | 403 | recon-run #42 |
| staging.target.com | 200 | manual upload |
The details that keep you in the loop
Historical scan results
Every run is archived. Compare results across versions, spot diffs on your targets, and never lose a finding again.
Centralized notifications
Scan findings, dataset triggers, and bhlast interactions land in one inbox, so the important stuff finds you.
Blob storage
Securely store and manage large files, binaries, and artifacts right next to your projects and workflows.
Ready to Automate Your Hunting?
Join security researchers automating recon, scanning, and OOB monitoring with BountyHub. Build your first workflow today.